
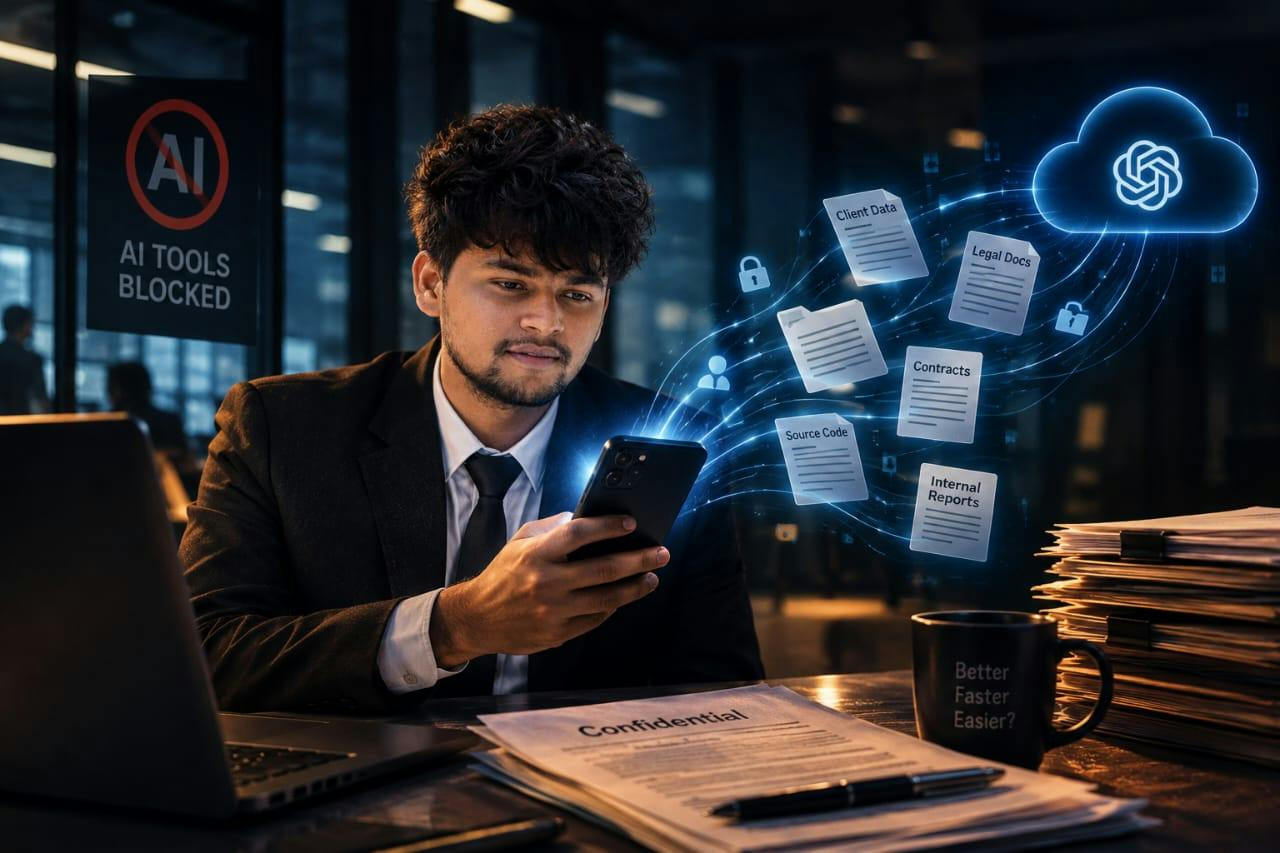
It is 1:45 AM. A junior associate is sitting at their desk, trying to finish a 110-page agreement that has to be ready by 8:00 AM. The coffee has gone cold. After hours of reading the same pages, even simple clauses are becoming difficult to understand. There is still a lot of work left, and very little time. The associate opens a free AI chatbot on a personal phone and copies three clauses from the agreement. Within seconds, the tool provides a short summary. The work becomes a little easier, and the associate moves on to the next task. But there is one problem. The law firm has already banned the use of public AI tools. Its computers block access to these websites, and employees have been warned not to use them for professional work. Yet the associate has found another way to access the same tool through a personal device. The firm's system may show that its restrictions are working. But it cannot necessarily show what the associate has shared through a personal connection. This is one way Shadow AI can enter a workplace. The employee may not intend to expose confidential information. They may simply be trying to finish an urgent task. But the information has still moved outside the organisation's control. And this raises a question that companies need to consider: If employees are still finding ways to use AI despite a workplace ban, is blocking access really enough to protect the organisation? Understanding the Shadow AI Problem Shadow AI refers to the use of artificial intelligence tools by employees without the knowledge or approval of their organisation. These tools may include public chatbots, AI writing assistants, browser extensions, coding tools and meeting transcription applications. The problem is not limited to which tool an employee uses. It is also about what information they share with it. An employee may upload a client document to get a summary, enter company data to prepare a report, or share a section of source code to find an error. These actions may appear harmless from the employee's point of view. However, the organisation may have no clear understanding of where that information goes, how it is stored or what happens to it after the task is completed. Many companies have responded by restricting or blocking public AI platforms. Their concerns are understandable. Confidential information, customer records and business documents should not be shared with services that have not been properly assessed. However, a restriction does not automatically change employee behaviour. If a company blocks an AI website but continues to expect employees to complete the same workload within the same deadlines, the reason for using AI does not disappear. Some employees may simply find another way to access it. This is where the real problem begins. A company may successfully block an application on its office network while remaining unaware that employees are using the same application through personal phones, private accounts or other connections. Banning AI may restrict access through official systems, but it does not necessarily stop its use. In some situations, it can move that use beyond the organisation's visibility. The use of AI at work is growing faster than many organisations can introduce their own systems and policies. Microsoft and LinkedIn's 2024 Work Trend Index reported that 75% of global knowledge workers were using AI at work. Among those using AI, 78% were bringing their own AI tools to work, commonly described as Bring Your Own AI (BYOAI). This pattern aligns with broader enterprise trends. Research from Gartner shows that over 41% of employees actively acquire, modify, or use technology outside the visibility of IT department. These figures are important because they show that employees are not waiting for their organisations to introduce every tool they want to use. But they should be understood carefully: they show workplace AI adoption and the use of personal tools; they do not prove that corporate bans are the reason employees use them. The reasons can be practical. A legal associate may want to understand a long agreement more quickly. A researcher may need to organise a large amount of information. A software engineer may want help finding an error in code. An employee preparing a presentation may use AI to create an initial draft. In each case, the employee is trying to save time or complete a task more efficiently. This does not make every use acceptable. Employees still have a responsibility to follow workplace policies and protect confidential information. But organisations also need to understand why employees are turning to tools that have not been approved. A policy that only says "do not use AI" may not answer the questions employees face every day: Which tools can I use? What information can I share? What should I do when the approved system cannot handle my task? When these questions remain unanswered, employees may make their own decisions. That is how a technology policy can become disconnected from actual workplace behaviour. The Samsung Incident: When Workplace Use Becomes a Data Risk In April 2023, Samsung Electronics reportedly faced incidents in which employees entered sensitive internal information into ChatGPT. Reports described employees sharing semiconductor source code and internal meeting information while using the tool for work-related tasks. The incident became an important warning for companies considering the use of public AI platforms. It showed that sensitive information can leave an organisation through an ordinary workplace activity. An employee does not need to hack a system or deliberately attack a company. Copying information into an external chatbot can itself create a serious exposure. Samsung's response included restrictions on generative AI use. The incident demonstrates why companies became concerned about employees using public AI tools. It does not, by itself, prove that bans push employees towards personal devices. That is a separate issue that organisations need to examine through evidence about employee behaviour. There is another important point here. When information is entered into an external AI service, the organisation needs to understand the service's data practices. Different AI providers have different terms and settings. Some services may use submitted content for model improvement under certain conditions, while others offer business arrangements with different data-retention and training terms. It would be incorrect to assume that every public AI service handles every prompt in the same way. The concern is that employees using personal accounts may not know which terms apply to their information. The organisation may also have no contract, security review or clear process through which it can manage that risk. What Is Actually at Risk? For companies and legal institutions, Shadow AI is not just an IT concern. It can affect confidential information, legal responsibilities, customer trust and business interests. 1. Confidentiality and Attorney-Client Privilege Legal professionals regularly work with sensitive information. This includes client communications, draft agreements, litigation strategies, personal records and documents that have not been made public. Uploading such material to an external AI service without proper approval can create serious confidentiality concerns. However, it is important to distinguish confidentiality from attorney-client privilege. Sharing privileged information with a third-party service does not automatically waive privilege in every situation. The legal result depends on the jurisdiction, the circumstances of disclosure, the service provider's access and the steps taken to maintain confidentiality. Even where privilege is not automatically lost, sharing client information without proper safeguards may raise professional, contractual or ethical concerns. For a law firm, the question should therefore not be limited to whether an AI tool gives a useful answer. It should also ask whether the information being shared is permitted to leave the firm's controlled environment. 2. Data Protection and Financial Penalties The risk becomes more serious when employees share personal information through unapproved AI tools. For example, a document may contain a client's name, address, financial details, identification information or other personal data. If that information is sent to an external service without appropriate safeguards, the organisation may face data-protection questions. India's Digital Personal Data Protection Act, 2023 provides for penalties for specified failures. Under its Schedule, failure to take reasonable security safeguards to prevent personal data breaches can attract a penalty of up to ₹250 crore. This does not mean that every employee's use of an AI chatbot automatically leads to that penalty. The relevant legal duties, facts and circumstances must be considered. Similarly, under the European Union's General Data Protection Regulation (GDPR), certain serious infringements can attract fines of up to €20 million or 4% of the undertaking's total worldwide annual turnover, whichever is higher. These figures show why organisations need to take the handling of personal information seriously. But financial penalties are only one part of the problem. A data incident can also affect customer confidence, business relationships and the organisation's reputation. IBM's 2023 Cost of a Data Breach Report estimated the global average cost of a data breach at $4.45 million. This is a figure from the 2023 report, not a current estimate specifically for Shadow AI incidents. It nevertheless gives an idea of the financial impact that data breaches can have on organisations. 3. Loss of Trade Secret Protection Companies often hold information that gives them an advantage over competitors. It may include source code, product designs, pricing strategies, financial models, customer information or future business plans. Keeping such information confidential is an important part of protecting trade secrets. If employees regularly enter this material into public AI tools without checking the provider's terms or the organisation's security arrangements, the company may weaken its ability to show that it took reasonable steps to protect the information. The legal position will depend on the relevant law and circumstances. But the business concern is simple: information that was meant to remain inside the organisation may be shared with an external service without proper control. Why Blanket Bans May Not Solve the Problem Blocking AI websites may appear to be the easiest response. A company can restrict access through its network, issue a policy and warn employees against using unapproved tools. But consider the earlier example of the junior associate. Blocking a website on a company laptop does not prevent the associate from opening the same website on a personal phone. A personal hotspot can also take the activity outside the company's network. The organisation may see that its office systems are following the policy. It may not see what is happening elsewhere. This creates a difference between controlling access and controlling actual use. A company that provides approved AI tools can set rules about who can use them, what information can be shared and which security measures apply. It can also review usage through appropriate technical controls. By contrast, when employees use personal accounts and devices, the organisation may lose access to important information about that activity. It may not know which tools are being used, what information has been shared or whether an incident has taken place. This does not mean companies should allow every AI tool. Some uses should remain prohibited, especially where sensitive information cannot be adequately protected. But treating a ban as the complete solution overlooks the reasons employees may continue using AI. The issue is not simply whether an organisation permits or prohibits AI. It is whether its policy gives employees a safe and practical way to complete their work. A Practical Way Forward: From Bans to AI Governance Companies need a system that protects information without ignoring the way employees actually work. This does not require unrestricted AI access. It requires clear rules, suitable tools and safeguards that match the sensitivity of the information. 1. Provide Approved Enterprise AI Tools If employees are using public AI tools because they need help with everyday tasks, organisations should consider providing approved alternatives. Enterprise AI services may offer different contractual and technical protections, including limits on data retention and commitments about whether customer inputs are used for model training. Some providers also offer Zero Data Retention (ZDR) arrangements. However, companies should read the actual service terms instead of assuming that an enterprise label or ZDR promise guarantees complete privacy. They need to understand what data is retained, what logs are created, who can access the information and which settings are enabled. The aim is to give employees a reliable tool for their daily work without making them depend on personal accounts or unapproved services. 2. Use Local AI Models for Highly Sensitive Information Some work involves information that should not be sent to an external AI service. This may include sensitive source code, confidential legal strategy, certain client documents or important business information. For such work, organisations can consider running AI models on their own infrastructure or within a controlled private environment. Open-source model families such as Llama and Mistral may be considered for internal deployment, depending on the organisation's technical needs and resources. For particularly sensitive work, a disconnected or air-gapped system may offer an additional layer of protection. But local deployment is not automatically safe. The organisation still needs to manage access, system security, updates and the information employees enter into the model. 3. Create a Clear Data Classification System Employees should not have to guess whether a document can be shared with an AI tool. Organisations need to make these rules clear so that employees can understand what information is safe to share and what needs protection. One practical way to do this is dividing information into three categories: public, internal and condidential. Public information, such as published reports, press releases, and public case laws, can be used with apporved public or enterprise AI tools. Internal information, including routine meeting notes and general internal dragts, should only be used with AI tools approved under company policy. Confidential information, such as client records, personal data, contracts, source code and M&A information, requries greater care. Employees should use restricted tools or seek additional approval before sharing them. This system should be easy to understand and connected to the organisation's existing confidentiality rules. Legal teams may need additional restrictions for privileged communications, litigation material and client documents. 4. Use Data Loss Prevention Tools Data Loss Prevention (DLP) tools can help organisations identify and control the sharing of sensitive information. For example, these tools can detect personal indentification numbers, financial details or confidential information in data being sent to external AI services. Depending on how the system works, it may block the request, flag it for review or remove senstive information before it reaches an external service. These tools are not perfect. They may miss information or flag material that is harmless. They should therefore support, rather than replace, clear policies and employee awareness. 5. Make Employees Part of the Process Even a well-designed policy can fail if employees do not understand how to follow it in their daily work. Organisations should explain which AI tools are approved, what information must not be shared, when human review is required and how employees can request access to a new tool. They should also create a simple way for employees to report accidental disclosure. If people are afraid to report mistakes, organisations may learn about incidents too late to respond effectively. At the same time, employees must remain responsible for following the rules. Practical alternatives do not remove the duty to protect confidential information. Organisations need both clear expectations and fair accountability. Conclusion Shadow AI is not going to disappear simply because an organisation blocks access to certain AI tools. Employees still have deadlines, daily tasks and work to complete. When approved tools are unavailable or difficult to use, some may look for other ways to get the same work done. This creates a problem for organisations. They may have rules against using unapproved AI services, but those rules do not necessarily tell them where employees are actually using AI or what information they are sharing. This does not mean employees should be free to use any tool they want. Confidential information still needs protection, and employees must take responsibility for how they use AI. But organisations also need to look at why employees are turning to tools outside the approved system. If a tool is helping employees complete routine work more easily, the organisation should consider whether it can provide a safe alternative. It should also make clear what information can be shared and where approval is required. The real issue is not just whether employees are following AI policies. It is whether those policies work in the way people actually do their jobs. If organisations want to manage Shadow AI, they need to understand its use rather than simply try to stop it.
Shadow AI in the Workplace: Data Security Risks and Governance Strategies
Full Article
Original Source
Read the full article at Hackernoon →KhanList aggregates and links to publicly available news content. We do not host full articles from third-party sources. Always verify important information with original sources.