
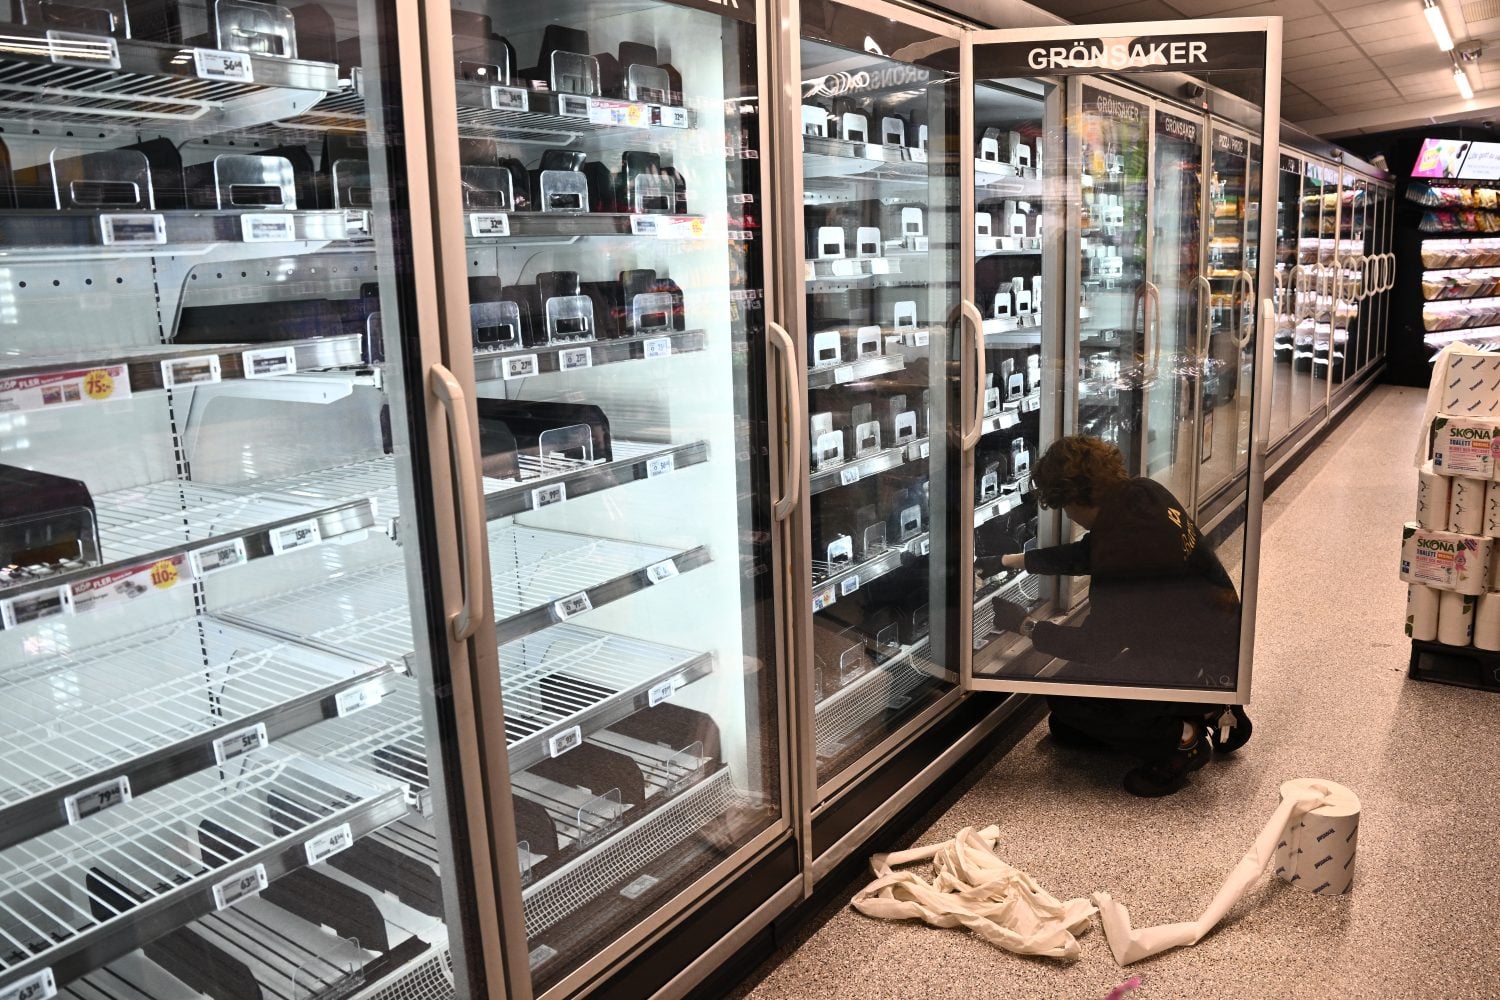
On the morning of Nov. 11, some 6,000 Italian schools received an identical email from a “Mikhail Andropov.” A “powerful explosive device with a remote trigger” had been left inside the building, the message said, and the survivors would be finished off with knives. Principals evacuated students from Trieste to Palermo. That same morning, more than 300 schools in Northern Ireland also received threatening emails, and police in Scotland reported similar bomb threats, as well. By midday, Italian Prime Minister Giorgia Meloni had convened an emergency meeting with Italy’s intelligence services and National Cybersecurity Agency at Palazzo Chigi in Rome. No bombs were found. Five days earlier, emails bearing the same signature and subject line (“Message to the West”) reached newsrooms in Ireland and Bulgaria, leading the Irish public broadcaster RTE to evacuate its offices and suspend programming. The emails claimed responsibility for a wave of false threats that, between Nov. 3 and Nov. 6, targeted at least 35 passenger flights across Europe. On Nov. 5 alone, around 20 civilian aircraft were affected: Italian, French, and Bulgarian fighter jets scrambled to escort airliners, and an Aer Lingus flight from Dublin to Rome was diverted to a French military air base. Italian schools had already been targeted on Oct. 19 and again on Nov. 2, when an email with the same text reached nearly 280 education facilities. In October, hundreds of schools in Britain, Hungary, and Serbia received similar threats. On the morning of Nov. 11, some 6,000 Italian schools received an identical email from a “Mikhail Andropov.” A “powerful explosive device with a remote trigger” had been left inside the building, the message said, and the survivors would be finished off with knives. Principals evacuated students from Trieste to Palermo. That same morning, more than 300 schools in Northern Ireland also received threatening emails, and police in Scotland reported similar bomb threats, as well. By midday, Italian Prime Minister Giorgia Meloni had convened an emergency meeting with Italy’s intelligence services and National Cybersecurity Agency at Palazzo Chigi in Rome. No bombs were found. Five days earlier, emails bearing the same signature and subject line (“Message to the West”) reached newsrooms in Ireland and Bulgaria, leading the Irish public broadcaster RTE to evacuate its offices and suspend programming. The emails claimed responsibility for a wave of false threats that, between Nov. 3 and Nov. 6, targeted at least 35 passenger flights across Europe. On Nov. 5 alone, around 20 civilian aircraft were affected: Italian, French, and Bulgarian fighter jets scrambled to escort airliners, and an Aer Lingus flight from Dublin to Rome was diverted to a French military air base. Italian schools had already been targeted on Oct. 19 and again on Nov. 2, when an email with the same text reached nearly 280 education facilities. In October, hundreds of schools in Britain, Hungary, and Serbia received similar threats. Some European intelligence officials consider Russia the most likely origin based on motive, modus operandi, and precedent. At the same time, these officials warn that a firm attribution may never come. Naturally, Moscow has denied involvement. Until a few weeks ago, the debate on Russia’s attacks on Europe was about the violent end of the spectrum: explosive-laden drones targeting a cargo plane in Leipzig, Germany; sabotage of railroad systems in Germany, the Netherlands, and Poland; drones over airports and military bases. These operations crossed into direct physical attacks and required capabilities that few actors possess. The past month shows the opposite end. A hoax bomb threat requires an email account and a few minutes, whereas the cost for the target is enormous: evacuations, bomb-disposal teams, aircraft diversions, fighter-jet scrambles, lost school days, and frightened parents. The authors of the “Message to the West” boasted of having caused widespread panic and forcing European authorities to spend a fortune on their emergency procedures. This perfectly illustrates the asymmetry of hybrid threats. The defender cannot dismiss the threat because of its potential catastrophic impact, so every hoax triggers the full precautionary protocol. The attacker sets the tempo while the defender can only react and bear the cost. A second feature makes this part of the hybrid war harder to counter. Schools, airports, and shopping centers in Europe receive their constant dose of empty threats from pranksters, students hoping to skip an exam, extortionists, and people with personal grievances. Each false alarm shows others how easy it is to cause disruption for free. On Wednesday, Italian Defense Minister Guido Crosetto predicted that such hoaxers will only multiply. Some of the threats against passenger flights claimed to come from the Male State, an anti-feminist movement banned in Russia. The claim of origin reads as mockery but also makes a point: No matter who is behind them, the hoaxes absorb resources and reinforce the perception of insecurity. For an attacker, each new campaign builds on the destabilizing effects of all previous ones. This is why the low end of the attack spectrum is a useful reminder of what hybrid campaigns are for. Their purpose is psychological, the target is public opinion, and the objective is to generate confusion, fear, and distrust in institutions. A drone strike and a fake email serve the same purpose by different means. The first tests how far the threshold of attacks that Europe will tolerate without responding has moved. The second shows how little it takes to make citizens feel unprotected. Meloni put it plainly on Wednesday: The threats, she said, appear to be part of a strategy to generate alarm and concern. The hoaxes also expose the attribution problem more starkly than sabotage does. Attribution is both a technical and a political issue. Pure data and forensic analysis rarely provide certainty about the sender. The senders of this month’s threatening emails have worn three masks: Iran’s Revolutionary Guards on Nov. 2, the Male State on Nov. 5, and a pseudonym evoking a long-dead Soviet leader since Nov. 6. Some of last week’s emails to airports came from an address at a public health network in the Colombian capital, Bogotá. And even when the attack’s origin is clear, government leaders often lack the political will to name the attacker. The reason usually given is fear of escalation. A second reason is rarely admitted: Naming the attacker would mean telling their publics that Russia has already escalated a war against Europe, and that this war demands a response. This creates a hard problem for policy. Against a threat with such disproportionate costs for the attacker and defender, reactive defense is a losing strategy. This is especially true given the fact that widely accessible technology makes these attacks ever cheaper to carry out at scale. The logical answer is deterrence, which means raising the cost and risk for the attacker. But deterrence rests on attribution, which will often be only partial. A credible deterrent posture therefore requires a degree of political courage that European governments have so far avoided. It means saying, in advance and together: We may not know with certainty who is behind the next wave, but if it happens, we will impose costs based on the available evidence, even if that evidence is incomplete. This is a probabilistic standard of response, closer to how intelligence works than how courts work. It is uncomfortable for democracies bound by the rule of law and accustomed to standards of incontrovertible evidence. And it carries a risk of error. The alternative is the certain continuation of a campaign that costs an adversary nothing and undermines the target every time. The posture must also be Europe-wide rather than national. A campaign that reaches Italian schools, Irish newsrooms, and Czech airports in the same week is designed to exploit divisions. A response that each country calibrates on its own invites the attacker to probe for the weakest link. The final element is speed. Because hybrid campaigns rely on diffused costs and dispersed information, they have to be met with rapid information sharing. When thousands of schools receive the same threatening email at the same moment—and that fact is known within minutes by everyone concerned—then the threat largely diagnoses itself: It is a coordinated campaign, and the alarms are very likely false. Italy’s education minister, Giuseppe Valditara, said as much on Wednesday, noting that the sheer number of schools involved demonstrated how little credibility the threat had. A similar logic applies to real attacks. When hackers took control of refrigeration systems in hundreds of French supermarkets in October and in stores across at least 11 European countries in early November, the pattern was the clue: It was a simultaneous, automated, and cross-border effort. A shared picture in real time turns hundreds of isolated emergencies into a single recognizable event. It speeds up the response, lowers the payoff for the attacker, and eases the attribution on which deterrence depends. At the European level, most of this civilian information sharing and coordination infrastructure does not yet exist. In the last two months, we have witnessed two very different ways in which hybrid campaigns exploit free societies as targets for attack. At one end, Europe’s adversaries are testing how much violence it will absorb before it reacts. At the other, they show how cheaply European societies can be disrupted. Both types of attacks are aimed at citizens’ confidence that their institutions can protect them. Europe can answer at both ends, but only if it finds the unity and political will to do it.
Russia’s Cheapest Weapon in Its Hybrid War Is Fear
Full Article
Original Source
Read the full article at Foreignpolicy →KhanList aggregates and links to publicly available news content. We do not host full articles from third-party sources. Always verify important information with original sources.